Engineering service
Automotive cyber security
Integrate cyber-security work into product engineering with practical support for risk, architecture, evidence and standards alignment.
Contact an engineer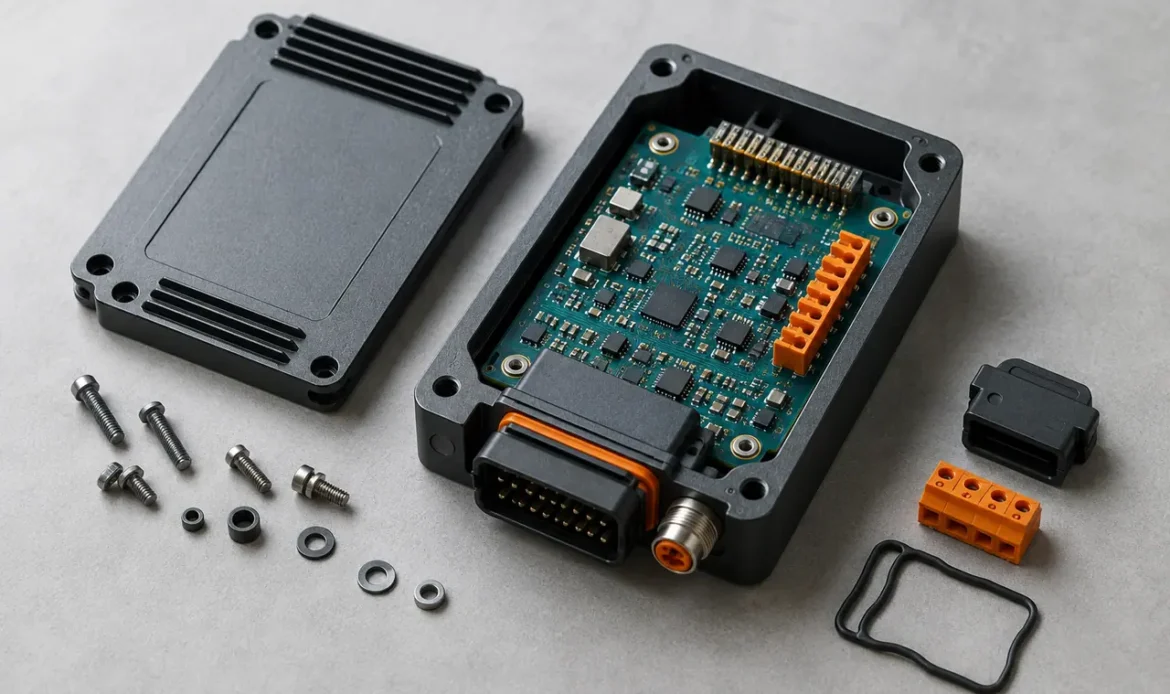
Illustrative engineering concept, not a completed client project.
Where DVAR can help
- A product programme needs a clear cyber-security engineering plan.
- Threat analysis needs to connect to real architecture and verification work.
- Supplier evidence needs review against programme and regulatory expectations.
Capabilities
- Cyber-security planning and work-product review
- Threat analysis and risk assessment support
- Security concepts and architecture input
- Verification and vulnerability-assessment planning
- Supplier evidence and engineering review
- ISO/SAE 21434 and UN R155 alignment support
What you receive
Deliverables are agreed for the project stage and designed for practical review, use and handover.
- Risk and planning work products
- Architecture and requirement review findings
- Verification recommendations and evidence review
- Clear actions for programme owners and suppliers
Plan the work around the evidence
Start with what exists and agree what the next development milestone needs to demonstrate.
Share an outline requirement, current design stage and the main constraint. Detailed files can follow through an agreed channel.
Agree the scope, interfaces, deliverables and acceptance criteria before detailed development begins.
Review the design information and test evidence against the agreed requirement, with clear actions for the next stage.
Before you enquire
Can you review existing cyber-security work products?
DVAR supports cyber-security planning, supplier evidence and work-product review. The scope is set around the programme requirements, available evidence and decisions that need to be made.
Does the service provide certification?
The service provides engineering and alignment support for ISO/SAE 21434 and UN R155. It does not promise certification or regulatory approval; programme obligations and approval responsibilities must be established separately.
How does the work connect to product engineering?
Threat analysis and risk assessment inform security concepts, architecture input and verification planning. Findings are translated into actions for programme owners and suppliers.
Start with the next useful decision.
Share the requirement, current evidence and the risk you need to resolve.